Lost or Stolen Business Device? A Practical Response Checklist for UK SMEs

Managed office devices with a security lock displayed after a business laptop goes missing

A laptop left on a train, a phone taken from a vehicle or a tablet that cannot be found can quickly become a business security incident. The device itself can be replaced. The more important questions are what it contained, which accounts it could access and whether anyone else can use it.

The response does not need to be chaotic. A clear process, supported by device management and accurate records, can help a business contain the risk and restore the user safely.

Why the first hour matters

Do not wait until the next working day in the hope that the device turns up. The person who notices the loss should report it to the organisation’s IT contact immediately, even if they are unsure whether it has been misplaced or stolen.

Early action gives the support team a better chance to lock the device, revoke active sessions and review recent activity before information disappears from logs. It also starts a reliable incident record if the loss later needs to be reported to an insurer, the police or the Information Commissioner’s Office (ICO).

1. Record the essential facts

Start a simple incident log and record facts rather than assumptions:

  • the user’s name and contact details;
  • the device type, make, asset number and serial number, if known;
  • when and where it was last seen;
  • whether it was locked, switched on or connected to a network;
  • which email, cloud, finance or business systems it could access;
  • whether files were stored locally; and
  • whether the device held personal, confidential or commercially sensitive information.

An up-to-date asset register makes this much quicker. It should connect each device to its assigned user, management status, encryption state and replacement history.

2. Lock, locate or erase the device

If the device is enrolled in mobile device management (MDM), an administrator may be able to put it into a lost mode, lock it or erase it remotely. The right action depends on the circumstances. Location information might help recover a misplaced device, while a remote wipe may be more appropriate when theft is likely or the information risk is high.

The National Cyber Security Centre explains that an MDM-enrolled device can receive a remote-wipe command when it is powered on and has a data connection. A wipe is not guaranteed to happen immediately if the device remains offline, so it should be one part of the response rather than the only control. See the NCSC guidance on erasing devices.

Do not attempt to confront someone shown at a device’s reported location. Pass relevant information to the police where theft is suspected.

3. Secure the user’s accounts

A locked screen does not necessarily end every active cloud session. Review and, where appropriate, revoke the device’s access to:

  • Microsoft 365 or Google Workspace;
  • business applications and file-sharing services;
  • remote-access and VPN services;
  • password managers;
  • finance, payment and customer systems; and
  • administrator or supplier portals.

Reset credentials where there is a credible risk of exposure, beginning with privileged accounts and the user’s primary email account. Check that multi-factor authentication remains under the user’s control and that no new authentication method or forwarding rule has been added.

Review sign-in and security logs for unusual locations, downloads or configuration changes. Preserve anything suspicious rather than deleting it, because it may help establish what happened.

4. Decide whether personal data may be affected

Losing a device does not automatically mean that data has been accessed, but the organisation still needs to assess the risk. Consider the strength of the screen lock and encryption, the sensitivity of the information, whether the device was remotely managed, and the likelihood that an unauthorised person could use it.

The ICO says organisations must keep a record of personal data breaches, whether or not a report is required. If a breach is likely to risk people’s rights and freedoms, the ICO must be notified as soon as possible and, where feasible, within 72 hours. If the likely risk is high, affected people must also be informed without undue delay. The ICO provides a small-business guide to the first 72 hours and a personal data breach self-assessment.

This assessment should be made by an appropriately authorised person and, where necessary, with legal or data-protection advice. Record the reasoning even when the decision is not to report.

5. Restore the user safely

The priority is to get the person working again without recreating the same risk. Supply a known, managed replacement rather than allowing an unprotected personal device to become a permanent workaround.

Restore approved business data from a verified backup or managed cloud service. Reapply security policies, software updates, endpoint protection, encryption and access restrictions before returning the user to normal work. If the missing device later reappears, do not reconnect it automatically; let IT inspect and re-enrol it first.

Controls to put in place before the next incident

The easiest incident to manage is one for which the business is already prepared. A sensible baseline includes:

  • full-disk encryption and a strong automatic screen lock;
  • MDM or another suitable management platform for company devices;
  • multi-factor authentication for important accounts;
  • least-privilege access, with separate administrator accounts;
  • an accurate asset register and clear joiner, mover and leaver processes;
  • tested backups for important business data;
  • a written lost-device and personal-data-breach procedure; and
  • staff training that makes prompt reporting easy and blame-free.

These controls should cover the complete workplace. Windows PCs, Macs, iPhones, iPads and Chromebooks use different management tools, but the business outcome is the same: know what you own, apply a consistent security baseline and retain the ability to remove access when a device is no longer trusted.

A simple lost-device action plan

When a device goes missing, remember this sequence:

  1. Report it immediately.
  2. Record the facts and the systems involved.
  3. Lock, locate or wipe the device where appropriate.
  4. Revoke sessions and secure affected accounts.
  5. Assess the information and personal-data risk.
  6. Preserve evidence and make any required reports.
  7. Restore the user on a known, managed device.
  8. Review what would make the next response faster.

Make device loss a manageable event

MSP247 supports mixed Windows, Apple and Chromebook environments alongside networks, Microsoft 365, backups and business continuity. We can help you review device management, encryption, account security, asset records and recovery arrangements as one joined-up service.

If you are unsure how quickly your business could contain a lost-device incident, book a free IT review or call 0330 301 0500.
How to Test a Business Continuity Plan: A Practical Exercise for UK SMEs

Yorkshire business team rehearsing an IT continuity and incident recovery plan

A business continuity plan can look perfectly sensible until something actually goes wrong.

During a genuine outage, people may discover that an important password is unavailable, the nominated decision-maker is on holiday, a supplier cannot be reached or the backup does not contain what everyone expected. These are expensive problems to uncover while customers are waiting and staff cannot work.

A tabletop exercise gives your team a safe way to rehearse an incident before it happens. It does not require anyone to disconnect live systems or simulate a technical attack. Instead, the people involved work through a realistic scenario, discuss what they would do and record the gaps that need attention.

What is a business continuity tabletop exercise?

A tabletop exercise is a structured discussion based on an unfolding incident. A facilitator introduces the situation in stages. Participants explain how they would respond, who they would contact, what decisions they could make and what information they would need.

The National Cyber Security Centre provides a free Exercise in a Box service covering scenarios including ransomware, phishing, supply-chain compromise and vulnerable systems. It is designed for organisations of different sizes and does not require participants to be cybersecurity experts.

The objective is not to catch people out. It is to find assumptions, unclear responsibilities and missing information while there is still time to correct them.

Choose one believable disruption

Begin with a scenario that could materially affect your organisation. Keep it specific enough to prompt decisions without turning the exercise into a technical examination.

  • Staff cannot access Microsoft 365 after several accounts are compromised.
  • A server or important cloud application becomes unavailable.
  • A ransomware warning appears on multiple computers.
  • The main internet connection fails during a busy working day.
  • A laptop containing business information is lost.
  • A critical supplier reports that its own systems have been breached.
  • Your premises cannot be accessed following a power, fire or security incident.

Choose the scenario that would have the clearest effect on customers, revenue, safety or essential operations.

Bring the right people together

A useful exercise normally needs more than the IT contact. Include people who understand how the organisation operates and who would have responsibilities during a disruption.

  • A senior decision-maker.
  • The person responsible for IT or the managed service provider.
  • Operations or service-delivery staff.
  • Finance or payroll.
  • Communications or customer service.
  • HR or data-protection responsibilities.

Nominate one person to facilitate the exercise and another to record decisions, unanswered questions and follow-up actions.

A practical 60-minute exercise

You can run a useful first exercise in approximately one hour.

1. Introduce the incident

It is 9:15 on Monday morning. Several employees cannot open shared files. Two computers display an unexpected ransom message, and a customer says an email from your finance team asked them to use a different bank account.

Ask who should be contacted first, how staff would report the problem, who has authority to make urgent decisions and whether any equipment or accounts should be isolated.

2. Add uncertainty

The main administrator account cannot be accessed. Your usual IT contact is unavailable, and it is not yet clear whether backups have been affected.

Discuss where emergency access details are kept, whether there is a second authorised contact, who can reach key suppliers and which services should be restored first. This stage often reveals that a technical control exists but nobody is certain who owns it or how it would be used.

3. Consider customers and communications

Telephone enquiries are increasing, and an important customer wants to know whether its information has been affected.

Decide who approves internal and external updates, how employees receive instructions if email is unavailable, and which customers, suppliers or insurers may need to be contacted. The NCSC recommends keeping a careful incident record, including decisions, actions and missing information. It also stresses the importance of clear communication with customers and other stakeholders during an incident. Read the NCSC incident-management guidance.

4. Work through recovery

  • Which data and systems are the highest priority?
  • What is the most recent acceptable recovery point?
  • Has the relevant backup ever been restored?
  • Are recovery credentials separate from everyday accounts?
  • Can the business operate from another location or connection?
  • Who decides when normal service can resume?

A green backup status is reassuring, but it is not proof that the required information can be restored within an acceptable time. Restoration testing should form part of the exercise where it can be performed safely. Our backup and business continuity service explains how recovery priorities and testing fit together.

Include personal-data decisions

A cyber incident does not automatically mean that a report must be made to the Information Commissioner’s Office. However, the team should know who will determine whether personal data has been affected and whether the reporting threshold is met.

For a notifiable personal-data breach, organisations must notify the ICO without undue delay and, where feasible, within 72 hours of becoming aware of it. Organisations must also keep records of personal-data breaches, including those that are not reported. See the ICO personal-data breach guidance.

Your exercise should identify who starts the incident record, who assesses the risk and where legal or specialist advice would be obtained.

Turn the discussion into an action plan

The exercise is only valuable if its findings lead to improvements. For every gap, record the required action, the person responsible, the completion date, the affected service and how completion will be checked.

Typical actions might include creating a second emergency administrator account, updating supplier contacts, testing a Microsoft 365 or server restoration, documenting call-diversion instructions or agreeing who can authorise emergency expenditure.

How often should an exercise be run?

There is no single schedule suitable for every organisation. As a practical starting point, consider an exercise at least annually and after significant changes to systems, premises, suppliers or senior responsibilities.

Use different scenarios over time. A ransomware discussion tests different decisions from a broadband failure, lost device or unavailable cloud supplier. Repeating an exercise after improvements have been made is an effective way to confirm that the original weaknesses have genuinely been addressed.

Make continuity something you can use

Business continuity should not be a document that is written once and forgotten. It should give people clear priorities, dependable contact routes and recovery arrangements they have seen work.

MSP247 helps organisations across Yorkshire review critical systems, backup arrangements, connectivity dependencies and incident responsibilities. We can also help structure a practical exercise and turn the results into a prioritised improvement plan.

Call 0330 301 0500 to discuss your current arrangements.

Passkeys for Small Businesses: A Practical UK Guide

Business colleagues using passkeys across laptops and a smartphone in a mixed-device workplace

Passwords remain one of the weakest points in business security. Staff reuse them, attackers steal them through convincing sign-in pages, and support teams spend time resetting them when they are forgotten.

Passkeys offer a practical alternative. They let someone sign in using the security already built into their phone, computer or hardware security key, without sending a reusable password across the internet.

The UK National Cyber Security Centre recommends choosing passkeys over passwords wherever they are available because they are resistant to phishing and cannot be intercepted or reused in the same way as a password. Read the NCSC’s passkey guidance.

That does not mean every business should immediately disable every password. A safe move to passkeys requires planning, testing and a reliable account-recovery process.

What is a passkey?

A passkey is a digital credential created for a specific website, application or online service. It consists of two related cryptographic keys.

The service keeps the public key. The private key remains protected by the user’s device, security key or approved password manager. When the user signs in, the device proves it holds the private key without revealing it.

The user normally authorises the sign-in with the same method used to unlock the device, such as Face ID, Touch ID, a fingerprint, a device PIN or a hardware security key.

The biometric information is not sent to the website or cloud service. It is checked locally by the device to unlock the passkey. Google’s Workspace guidance confirms that a fingerprint, face scan, PIN or pattern remains local and is not shared with Google or other parties. See Google Workspace passkey guidance.

Because a passkey is tied to the genuine website or application for which it was created, a fraudulent login page cannot simply collect and reuse it.

Where can a business use passkeys?

Support is already available across many of the platforms commonly used by small businesses.

Microsoft Entra ID supports both synced and device-bound passkeys. Credentials can be held in Microsoft Authenticator, on a FIDO2 hardware security key or through an approved passkey provider. Microsoft also allows administrators to target deployment at selected groups before extending it across the organisation. Review Microsoft’s current Entra passkey guidance.

Apple devices can store passkeys in iCloud Keychain and make them available across compatible iPhones, iPads and Macs using the same Apple Account. Apple requires two-factor authentication and iCloud Keychain to be enabled. See Apple’s UK passkey instructions.

Google Workspace administrators can allow users to skip password challenges and authenticate with a passkey stored on a phone, computer or security key. Administrators can also restrict deployment to hardware security keys where that is appropriate.

Availability still varies between applications. Older software, legacy email clients and some specialist services may continue to require passwords, so passkeys should be introduced as part of a wider identity-security plan.

A sensible passkey rollout for a small business

1. Start with the accounts that matter most

Begin with administrators, directors, finance users and anyone who can access sensitive customer information. These accounts present the greatest risk if their credentials are stolen.

Do not overlook shared cloud services, domain administration, backup platforms, remote-access tools and social-media accounts.

2. Review the devices people actually use

A passkey plan must reflect the real workplace. Check whether staff use managed Windows PCs, Macs, iPhones, Android phones or Chromebooks, and whether personal devices are permitted.

Decide whether passkeys may synchronise through personal accounts or whether company-controlled authenticators and hardware security keys are required.

3. Plan account recovery before deployment

A lost phone must not become a business emergency.

Privileged users should normally have more than one approved authentication method. This might include a second managed device, a spare hardware security key stored securely or an administrator-controlled recovery process.

Recovery must be documented, tested and protected from social engineering. An attacker who cannot steal a passkey may instead attempt to persuade someone to reset it.

4. Run a small pilot

Choose a group representing different roles and devices. Test everyday sign-ins, remote working, replacement devices and recovery.

The pilot should identify unsupported applications and unclear instructions before they affect the whole company. Record what users found confusing and improve the guidance before expanding the rollout.

5. Update joiner, mover and leaver procedures

Authentication credentials must follow the employment lifecycle. New starters need an approved enrolment process. Role changes may require different security controls, while leavers must have passkeys and active sessions removed promptly from company services.

Company-owned hardware security keys should be inventoried and recovered where possible.

6. Keep stronger controls for privileged access

Convenient synced passkeys can be suitable for many everyday users. Administrators or people handling particularly sensitive systems may benefit from device-bound passkeys or dedicated hardware security keys.

Microsoft describes FIDO2 security keys as an appropriate option for elevated and highly regulated users because the private key remains on the physical authenticator. Read Microsoft’s explanation of FIDO2 security keys.

7. Train staff in the new sign-in process

Passkeys reduce phishing risk, but people still need to understand what has changed.

Explain that staff should not approve unexpected recovery requests, scan unsolicited sign-in QR codes or disclose device PINs. Provide a clear route for reporting lost devices and suspicious prompts.

Passkeys are one part of good account security

Passkeys can make sign-in both safer and easier, but they do not replace device management, software updates, access reviews or reliable backups.

A compromised or unmanaged device can still expose business information after a legitimate user has signed in. Businesses should combine passkeys with:

  • Managed and encrypted devices
  • Prompt removal of unused accounts
  • Restricted administrator privileges
  • Regular access reviews
  • Secure recovery procedures
  • Monitoring for unusual sign-ins
  • Tested backup and incident-response arrangements

The objective is not simply to remove passwords. It is to create an authentication process that is easier for genuine users and substantially harder for an attacker to exploit.


Need help planning a safe rollout?

MSP247 supports businesses using Windows, Mac, iPhone, iPad, Chromebook, Microsoft 365, Google services and mixed-device environments. Our free business IT review can examine your current authentication methods, administrator accounts, device management and recovery arrangements.

Related services: managed IT support, Apple business IT support, Microsoft 365 support and management, and cybersecurity services.

Microsoft 365 Security Checklist for Yorkshire Businesses

Microsoft 365 security checklist for Yorkshire businesses

Microsoft 365 security begins with identity. If an attacker gains control of a user or administrator account, they may be able to read email, change rules, access shared files and impersonate the business. This checklist gives Yorkshire SMEs a practical starting point, but settings should be matched to licence, risk and operational needs.

Protect identities and administrator access

  • Require multi-factor authentication using appropriate modern methods
  • Block legacy authentication where it is not required
  • Use separate named administrator accounts
  • Keep emergency access arrangements tightly controlled and monitored
  • Review sign-in risk, unusual locations and repeated failures
  • Remove leavers promptly and review dormant accounts

Reduce email and collaboration risk

Review anti-phishing, impersonation and malicious-link protection. Configure email authentication for your domains and monitor reports. Users should know how to report suspicious messages without forwarding harmful content around the business.

Check external sharing in SharePoint, OneDrive and Teams. Public or anonymous links should be deliberate, time-limited where appropriate and reviewed regularly. Guest accounts need an owner and a business purpose.

Bring devices into the security boundary

Cloud controls are weakened if an unmanaged or infected device can download sensitive data. Maintain an inventory, require supported software, encrypt storage and apply appropriate device-management and endpoint-protection policies across Windows, Mac and mobile platforms. MSP247’s RMM supports all major platforms and helps identify health and update issues early.

Plan for recovery and investigation

Decide how long logs are retained and who will investigate an alert. Document the steps for a compromised account: disable access, revoke sessions, reset credentials, inspect forwarding rules, preserve evidence and communicate safely. Test the process before a real incident.

Retention settings and recycle bins are not automatically a complete backup strategy. Confirm whether independent backup is required for email, OneDrive, SharePoint and collaboration data, and test actual restores.

Review continuously

Security settings change as Microsoft adds features, licences are altered and staff join or leave. Schedule regular reviews of privileged roles, sharing, application consent, mail rules, device compliance and backup status. Record exceptions and assign an owner.

Turn the checklist into a prioritised plan

MSP247’s free business IT review includes Microsoft 365 security, backup, device management, connectivity and supplier gaps. We can identify quick wins and build a proportionate improvement roadmap for your organisation.

Cyber Essentials Preparation for Small Businesses

Cyber Essentials security controls protecting a small business

Cyber Essentials preparation is easier when it is treated as a structured improvement project rather than a last-minute questionnaire. The scheme focuses attention on five practical control areas that reduce exposure to common internet-based attacks. For a small business, the most useful first step is to define the assessment scope and establish an accurate inventory.

Know what is in scope

Document internet-connected devices, cloud services, user accounts, home workers, routers and firewalls. Include Windows PCs, Macs, smartphones, tablets, servers and supported virtual infrastructure. Unknown devices and forgotten administrator accounts are common reasons for uncertainty during preparation.

Decide whether the whole organisation will be assessed and make sure any proposed boundary is defensible. The goal is not to hide difficult systems; it is to understand risk and apply the required controls consistently.

Work through the five control themes

  • Firewalls and internet gateways: remove unnecessary services, review rules and change default credentials.
  • Secure configuration: disable unused accounts and features, use supported software and apply sensible device settings.
  • User access control: give people only the access they need, protect administrator accounts and use multi-factor authentication where required.
  • Malware protection: use appropriate security controls and restrict untrusted software.
  • Security updates: install high-risk updates within the required timescale and replace software that no longer receives fixes.

Gather evidence as you improve

Keep screenshots, configuration exports, asset lists and policy decisions in one place. Record how mobile devices and home networks are handled, how joiners and leavers are processed and who owns each action. Evidence makes the assessment more efficient and leaves the business with reusable operational documentation.

Do not confuse certification with permanent security. Controls can drift as users, devices and software change. MSP247’s all-platform RMM coverage helps monitor supported environments, raise alerts and maintain patch visibility after the initial preparation work.

Avoid overclaiming

Certification is a valuable baseline, not a guarantee that an organisation cannot be breached. It should sit alongside backups, phishing awareness, incident planning, supplier review and appropriate cyber insurance. Where questions touch legal or insurance obligations, take advice from the relevant professional.

Prepare with a clear action list

Our free business IT review can identify unsupported equipment, account weaknesses, backup gaps and device-management issues before you begin a formal Cyber Essentials submission. MSP247 can then help implement and document proportionate improvements across your Yorkshire business.

The 2025 Cyber Governance Code: A Practical Checklist for Business Leaders

Business leaders and an IT adviser reviewing cyber risk, suppliers and incident response

The UK government launched its Cyber Governance Code of Practice on 8 April 2025. It is aimed primarily at boards and directors because cyber security is not only a technical issue: an incident can stop operations, damage customer trust and create serious financial exposure.

The Code was designed for medium and large organisations, but its principles scale well to an SME. A small leadership team can apply them without creating a heavy governance process.

Give cyber risk a named owner

Someone at leadership level should own cyber risk and make sure it is considered alongside financial, operational and legal risks. Your IT provider can advise and operate controls, but the business must decide its priorities, acceptable risk and recovery expectations.

Know which services matter most

Identify the technology, information and suppliers that support essential activities such as taking orders, accessing customer records, paying staff and communicating with clients. Agree how long each activity can be unavailable and how much data loss the business could tolerate.

Ask for useful reporting

A long list of technical alerts is not board assurance. Leadership reporting should show trends and exceptions, including:

  • unsupported devices and overdue critical updates;
  • multi-factor authentication and endpoint-protection coverage;
  • backup success and restore-test results;
  • high-risk suppliers and outstanding remediation;
  • security incidents, lessons learned and repeat problems;
  • staff training completion and phishing-reporting behaviour.

Review the measures regularly and set clear tolerances. A red status should lead to an owner, action and deadline.

Include suppliers and cloud services

Most SMEs rely on external platforms and support partners. Record which suppliers can access sensitive data or administer systems, then confirm their security commitments, access controls, incident-notification process and exit arrangements. Remove third-party accounts when they are no longer required.

Practise the response

An incident plan is valuable only if people know how to use it. Run a short tabletop exercise based on a realistic scenario such as ransomware, a compromised mailbox or loss of the main internet connection. Include leadership, IT, communications and any critical suppliers. Record decisions and improve the plan after the exercise.

A quarterly leadership checklist

  1. Have our critical services or suppliers changed?
  2. Are our highest risks reducing at the agreed pace?
  3. Can we recover essential data and operations within our target time?
  4. Are serious incidents and near misses producing measurable improvements?
  5. Do we have a funded plan for unsupported technology and known gaps?

MSP247 can translate technical evidence into a practical improvement plan and clear management reporting. Our IT consultancy, managed support and connectivity services cover the whole operating environment. Contact us to arrange a cyber governance review.

Cyber Essentials Willow: What the April 2025 Requirements Mean for SMEs

IT administrator reviewing five security controls protecting a small business network

Version 3.2 of the Cyber Essentials requirements, known as Willow, took effect on 28 April 2025. It keeps the familiar five technical controls but updates the wording to reflect passwordless sign-in, remote work and the different ways vendors now fix security vulnerabilities.

The official NCSC Cyber Essentials resources remain the definitive reference. The practical message for SMEs is that security management must cover the complete working environment, not only computers inside the office.

The five controls have not changed

Cyber Essentials still focuses on firewalls, secure configuration, security update management, user access control and malware protection. These controls block many common attacks when they are implemented consistently across devices, cloud services and users.

What Willow added or clarified

Passwordless authentication

The guidance now explicitly recognises passwordless methods such as biometrics, physical security keys, one-time codes and push approvals. Passwordless does not mean authentication-free: the method must still provide strong assurance and be managed throughout the user lifecycle.

Vulnerability fixes are broader than patches

A vendor may fix a serious vulnerability with a configuration change, script, registry adjustment or another approved mechanism rather than a conventional software update. Willow makes it clear that these fixes are part of security update management. High-risk fixes still need prompt action, normally within the scheme’s 14-day window.

Software has a wider meaning

Operating systems and desktop applications are only part of the picture. Browser extensions, scripts, libraries, network software and router or firewall firmware can all be in scope. An accurate asset and software inventory is therefore essential.

Remote working is normal working

The updated terminology reflects hybrid organisations. Corporate and bring-your-own devices that access business data are generally in scope, wherever they are used. If the organisation does not control the network, the endpoint needs its own correctly configured firewall and appropriate security controls.

Prepare before starting the assessment

  1. Confirm the scope, including cloud services, mobile devices and remote workers.
  2. Remove unsupported software and record vendor support dates.
  3. Verify that critical vulnerability fixes are applied within policy.
  4. Review administrator accounts, third-party access and multi-factor authentication.
  5. Check firewall rules and remove services that no longer have a business purpose.
  6. Collect evidence as you work rather than immediately before submission.

Cyber Essentials is not a one-off tidy-up. The strongest approach is to make its controls part of normal managed IT operations.

MSP247 can assess your environment, close technical gaps and help maintain the controls across Windows, macOS, mobile devices, cloud services and networks. Explore our managed IT support or contact us to discuss Cyber Essentials readiness.

Backup vs Microsoft 365 Retention: What Businesses Often Miss

Microsoft 365 cloud retention compared with independent backup

Microsoft 365 provides resilient cloud services, but resilience is not the same as a complete business backup strategy. Retention, recycle bins, version history and independent backup all solve different problems. The gap becomes obvious only when someone needs an older file, a departed user’s mailbox or a clean copy from before an incident.

What Microsoft 365 retention does

Retention policies help an organisation keep or delete content according to business and compliance rules. They can protect messages and files from ordinary deletion for a defined period, and they are valuable for records management. However, policy design can be complex and coverage varies by workload, licence and configuration.

Recycle bins and version history are helpful operational features, but they have limits. They may not meet a long recovery window, provide simple cross-user restore or preserve every item in the way the business assumes. Retention is principally about governance; backup is principally about recoverability.

Why an independent backup can matter

A separate backup creates another recovery copy outside the normal day-to-day user workflow. It can reduce dependence on a single administrator account or configuration and give the helpdesk a clearer restore process for mailboxes, OneDrive, SharePoint and collaboration data.

  • Accidental or malicious deletion discovered late
  • Ransomware or mass file corruption
  • A user account removed before data was preserved
  • Retention settings changed incorrectly
  • A need to restore selected items quickly without disrupting current data

Questions to ask about your current protection

Start with outcomes, not product names. Which services are protected? How often is data copied? How long is it retained? Can individual emails, folders, sites and permissions be restored? Who receives failure alerts? Most importantly, when was a real restore last tested?

Backups that are never checked can create false confidence. Recovery tests should use representative data, record the time taken and confirm that the recovered information is usable. The result then feeds into your wider business continuity plan.

Retention and backup should work together

A sensible design often uses both: retention to meet governance requirements and an independent backup to provide operational recovery. The settings should reflect contractual duties, legal advice and how long the business can tolerate data loss. MSP247 can review this alongside identity security, device protection and continuity rather than treating it as an isolated product.

Find the gaps before a recovery is urgent

MSP247’s free business IT review includes Microsoft 365 security, backup and recovery arrangements, unsupported equipment, connectivity resilience and current supplier gaps. We can document what is protected today and recommend proportionate improvements for your Yorkshire business.

Integrate AI with Unifi and ONVIF Cameras for Unmatched Site Security – AI Port

Professional business security cameras connected to an AI analytics gateway

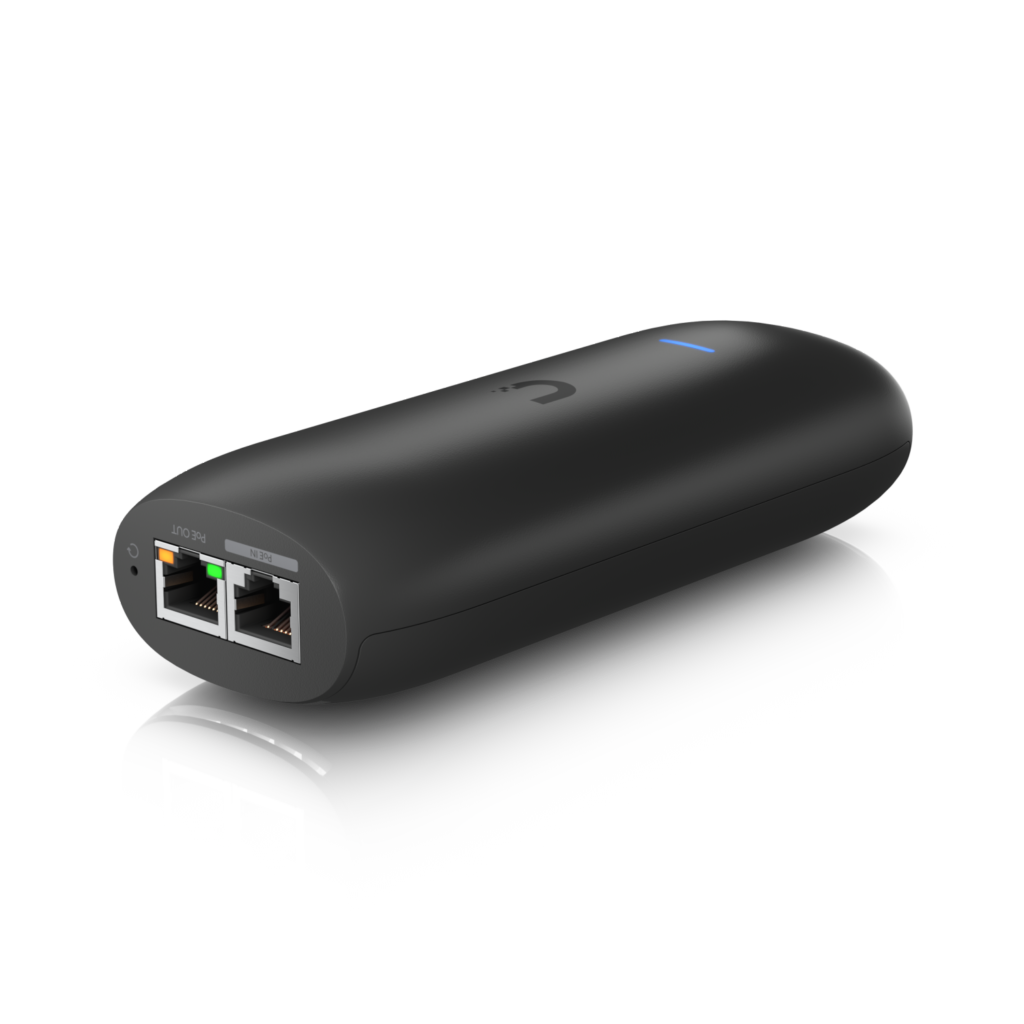
Introduction to the Unifi AI Port

In today’s rapidly evolving technological landscape, safeguarding business assets with cutting-edge surveillance solutions has become more crucial than ever. The integration of artificial intelligence with Unifi and ONVIF cameras marks a significant advancement in site security, offering unparalleled real-time monitoring and threat detection capabilities. With the new Unifi AI Port, businesses can seamlessly enhance their existing security systems, providing a robust layer of protection that is both intelligent and adaptable. This innovative technology not only supports Unifi cameras but also extends its compatibility to ONVIF third-party cameras, ensuring flexible and comprehensive coverage. By harnessing the power of AI, organisations can transform their safety protocols and ensure peace of mind.

AI Port

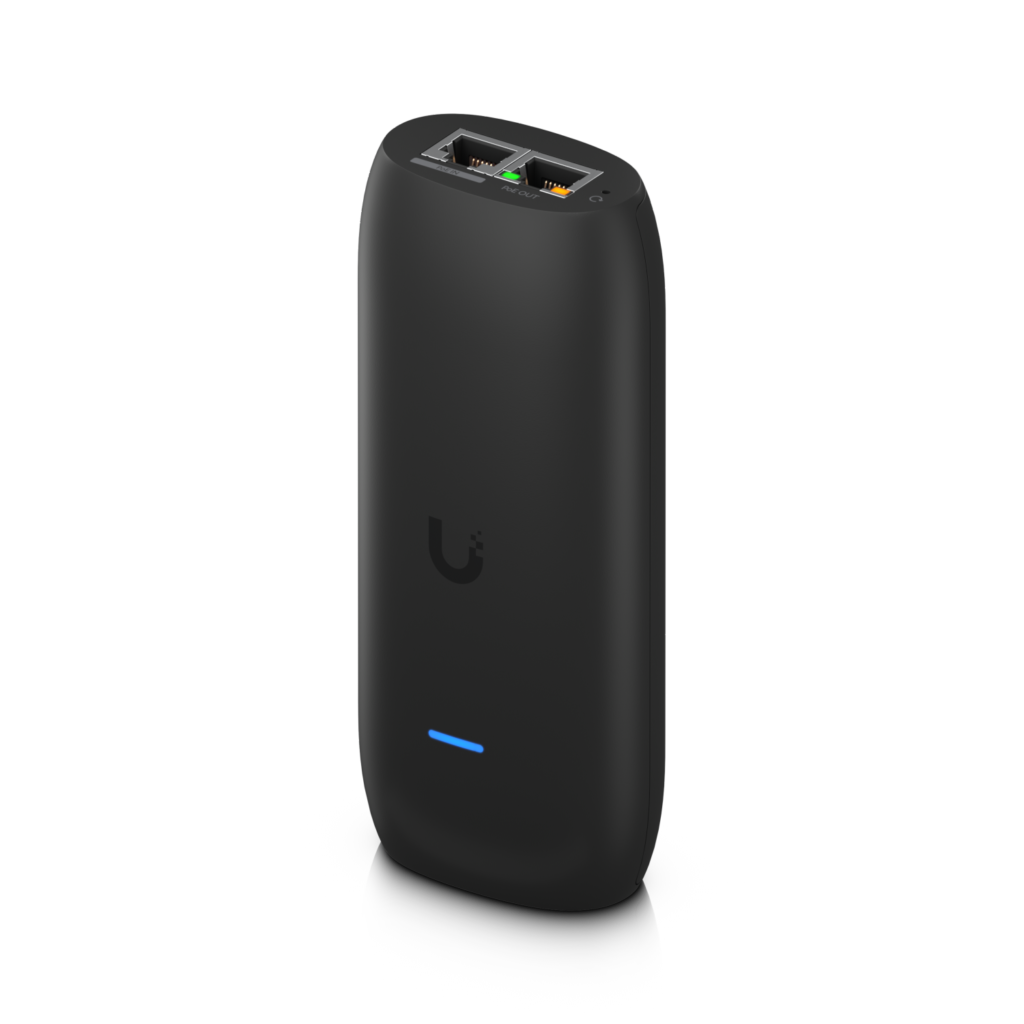
Specifications and Power Usage Options for the AI Port

The Unifi AI Port boasts impressive specifications:

  • Processor: Quad-core for high performance
  • Memory: 2GB DDR4
  • Storage: Comes with an SD card option for local recording, offering convenient on-device storage
  • Power Options: Supports PoE (Power over Ethernet) and a standard 12V DC power adapter
  • Connectivity: 1 Gigabit Ethernet port for high-speed network integration

AI Port Seamless Integration with Cameras

Direct Connection and Deployment

One of the standout features of the Unifi AI Port is its flexible deployment options. The AI Port can be deployed either by connecting directly to the network and to a camera, or by adding it to the network as a standalone device. You can then link the AI Port to the camera of your choice via the Unifi Console. This setup provides enhanced flexibility, allowing you to move the AI Port’s functionality from one camera to another as needed, making it a versatile tool for dynamic security environments.

AI Port Compatibility

The UniFi AI Port is a versatile tool designed to enhance the functionality of various camera systems by adding AI-driven detection capabilities. Here’s how it integrates with different camera types:

  • Non-AI UniFi Cameras
    • The AI Port extends AI capabilities to older UniFi cameras that do not have built-in AI features. This includes models like the UniFi G3 and G4 series that were not originally equipped with advanced AI processing.
    • By connecting these cameras to the AI Port, users can gain access to enhanced detection features such as person and vehicle detection, without needing to upgrade to newer, AI-enabled cameras
  • Third-Party Cameras
    • The AI Port supports third-party cameras through the ONVIF protocol, a widely-used standard for network cameras and video surveillance systems.
    • This compatibility allows users to integrate a broad range of non-UniFi cameras into their UniFi Protect ecosystem, enabling AI features like motion detection and object recognition on cameras from different manufacturers.
  • UniFi AI Camera Range
    • Cameras in the UniFi AI series, such as the AI Bullet, AI Dome, and AI 360, already have built-in AI capabilities. These models are designed to operate independently with advanced AI features directly integrated into the camera hardware.
    • The AI Port is not needed for these AI-enabled cameras, as they are already equipped with the necessary processing power and software to handle AI-based tasks like person detection, vehicle detection, and license plate recognition.
    • It’s important to verify camera compatibility before integrating the AI Port into your system to ensure optimal performance and avoid unnecessary hardware.

Current and Future Capabilities

  • Current Support: The AI Port currently supports either 1 Unifi camera or 1 ONVIF camera.
  • Possible Future Plans: Upcoming updates are expected to enable support for:
    • 5 x Unifi cameras
    • 3 x HD ONVIF cameras
    • 2 x 2K ONVIF cameras

Rack Option for Scalability

Unifi is planning to release a rack option that can accommodate up to 6 AI Ports, making it an ideal solution for larger setups requiring multiple ports.


Unifi AI Detection Types

UniFi AI technology leverages advanced artificial intelligence to provide a wide range of detection capabilities, enhancing security and monitoring systems. These features are commonly used across various scenarios to deliver accurate and actionable insights, minimizing false positives and improving overall efficiency. The key detection types include:

  • Person Detection: Identifies human presence in the camera’s view, ideal for distinguishing human activity from other movements.
  • Vehicle Detection: Detects and tracks vehicles, making it perfect for monitoring driveways and parking lots.
  • License Plate Recognition: Recognizes and records vehicle license plates for enhanced security and access management.
  • Intrusion Detection: Alerts when unauthorized entry is detected in designated areas, enhancing perimeter security.
  • Motion Tracking: Monitors and records movement, ensuring all activity is captured and analyzed in real-time.

Conclusion

The UniFi AI Port is a versatile and powerful addition to any security setup, designed to elevate the functionality of your surveillance system. It serves as a bridge, bringing advanced AI-driven features to both UniFi and ONVIF-compatible cameras, making it an invaluable tool for diverse security applications.

Key Benefits:

  • Enhanced AI Capabilities: The AI Port adds sophisticated detection features such as person detection, vehicle recognition, and motion tracking to cameras that lack built-in AI processing, significantly upgrading their functionality.
  • Seamless Integration: Whether you’re deploying UniFi cameras or third-party models using the ONVIF protocol, the AI Port ensures smooth and efficient integration into the UniFi Protect ecosystem, enhancing overall system coherence and usability.
  • Scalability: Suitable for both small and large-scale installations, the AI Port is designed to adapt to various security needs, whether it’s a single-site setup or a multi-location deployment. Its ability to support multiple cameras simultaneously makes it ideal for expanding surveillance networks without needing extensive hardware upgrades.

To learn more about how the Unifi AI Port can revolutionise your organisation’s security infrastructure, we invite you to reach out to us. Our team of experts is ready to provide detailed insights and tailored advice to ensure your business maximises the benefits of this advanced technology. Whether you’re looking to upgrade existing systems or install new surveillance solutions, we offer comprehensive support to meet your specific needs.

For more detailed information, or to schedule a consultation, please contact us at 0330 301 0500 or email sales@msp247.co.uk. We are committed to providing you with the best security solutions and support, ensuring your peace of mind and the safety of your assets.

Things you should know about Unifi Protect Cameras.

Modern office and warehouse protected by professionally positioned security cameras

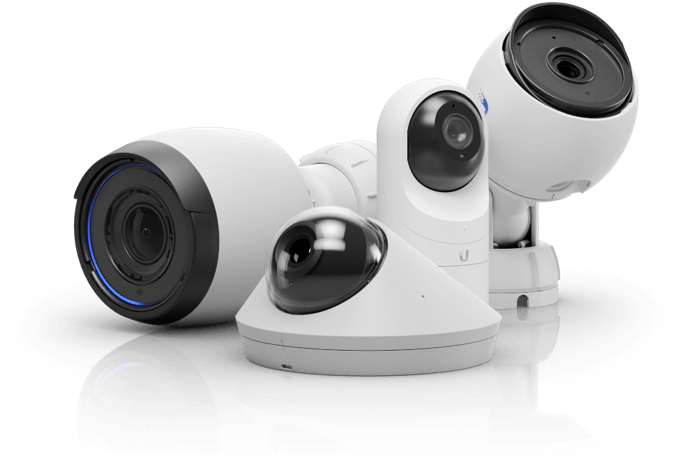
If you’re setting up a surveillance system, especially for a business, property, or home, UniFi Protect cameras are a popular choice due to their scalability, quality, and integration into a single ecosystem. But with multiple camera models available, how do you know which is right for your needs? In this guide, we’ll explore the full UniFi Protect camera range, compare different models within the line up, and discuss how they stack up against some third-party alternatives. We will also go over how Unifi Protect now support ONVIF third-party devices in a recent release.

As UniFi continues to expand its range of cameras, understanding the best options for different use cases is essential. In this blog, we explore the latest UniFi Protect cameras available on the official UK store, comparing features, connectivity options (Wi-Fi vs. Ethernet), and the ideal environments for each model.


UniFi Protect Camera Range Overview

Here’s a look at the most current line up of UniFi cameras, organized by series:

G4 Series:

  • G4 Bullet
  • G4 Instant
  • G4 Dome
  • G4 Pro
  • G4 PTZ
  • G4 Doorbell Pro

G5 Series:

  • G5 Bullet
  • G5 Dome
  • G5 Dome Ultra
  • G5 Flex
  • G5 Pro
  • G5 PTZ

AI Series:

  • AI Pro
  • AI 360
  • AI Theta
  • AI DSLR
Camera SeriesResolutionNight VisionConnectivitySmart FeaturesBest Use cases
G3 Series1080p (Full HD)IR, up to 10mPoEMotion detection, basic alertsEntry-level indoor/outdoor monitoring
G4 Series2K (4MP) / 4K (8MP)IR, up to 25mPoE (some Wi-Fi)AI object detection (person, vehicle), smart alertsAdvanced home/business security
G5 Series2K (4MP) / 4K (8MP)IR, up to 30mPoESmart detection (person, vehicle, package)High-performance surveillance
AI Series2K (AI 360) / 4K (AI Pro) / DSLR-quality (AI DSLR)IR, up to 50mPoEAI-enhanced motion detection, smart event classificationAI-driven analytics and facial recognition
IR = Infrared PoE = Power over Ethernet AI= Artificial intelligence

G3 Series (Entry-Level)

The G3 series is the most budget-friendly, designed for users who want basic surveillance without sacrificing quality. The cameras in this range offer:

  • Resolution: 1080p (Full HD).
  • Night Vision: Infrared (IR) up to 10 meters.
  • Connectivity: PoE (Power-over-Ethernet).
  • Smart Features: Motion detection and basic alerts.
  • Best for: Small businesses, residential properties, and users with basic surveillance needs.

While reliable, the G3 cameras lack advanced AI and object detection, making them less suitable for environments that require intelligent event categorization.

G4 Series (Mid-Range)

The G4 series steps up with improved video quality and smart features:

  • Resolution: Ranges from 4MP (2K) to 8MP (4K).
  • Night Vision: IR up to 25 meters, with options like the G4 Pro featuring high-performance night vision.
  • Connectivity: PoE, with some models (like the G4 Doorbell Pro) supporting Wi-Fi.
  • Smart Features: AI object detection, recognizing people, vehicles, and even packages.
  • Best for: Homes or businesses requiring advanced security monitoring with smart detection, such as monitoring vehicle access or entrances.

Notable Models:

  • G4 Pro: For large areas, thanks to its 4K resolution.
  • G4 Dome: Ideal for indoor environments due to its discreet design.

G5 Series (Next-Gen)

The G5 series is the latest and features several enhancements over the G4 series:

  • Resolution: 4MP (2K) to 8MP (4K), delivering ultra-clear images.
  • Night Vision: Enhanced IR with up to 30 meters of visibility in complete darkness.
  • Connectivity: PoE only, offering stable connections and simplified cabling.
  • Smart Features: Includes smart detection for people, vehicles, and packages, with enhanced AI event detection for fewer false alarms.
  • Best for: Users needing high-performance security for large areas, both indoor and outdoor, such as warehouses or large homes.

Notable Models:

  • G5 Bullet: Compact yet powerful for outdoor areas.
  • G5 PTZ: Perfect for expansive areas, with pan, tilt, and zoom capabilities.

AI Series (Premium, AI-Driven)

The AI series takes UniFi’s smart features to the next level, using advanced AI algorithms:

  • Resolution: From 4K Ultra HD to DSLR-quality video.
  • Night Vision: Superior night vision capabilities, with ranges up to 50 meters
  • .Connectivity: PoE for high-quality, reliable video streaming.
  • Smart Features: AI-enhanced event detection, with the ability to classify and track complex scenarios. The AI series is also designed to handle facial recognition tasks (though this feature is still under development for broader releases).
  • Best for: Large-scale surveillance environments that require advanced analytics, such as public spaces or high-security sites.

Notable Models:

  • AI Pro: Offers 4K video quality and AI-driven object detection.
  • AI 360: Provides a 360-degree field of view, ideal for large areas that need panoramic coverage.

Wi-Fi vs Ethernet: Why It Matters

Currently, most UniFi Protect cameras rely on Ethernet for connectivity, enabling stable connections and the option for Power over Ethernet (PoE), simplifying installation by removing the need for additional power cables. While Wi-Fi cameras provide more flexibility in placement, Ethernet ensures higher reliability, especially in environments with high data transmission or interference risks.


Mobile Access via the UniFi Protect App

One of the standout features of UniFi cameras is the UniFi Protect app. Available on both iOS and Android, this app allows users to manage and view live feeds remotely.

Key benefits include:

  • Real-Time Notifications: Receive alerts when motion is detected or AI events (like package detection) are triggered.
  • Remote Monitoring: View live feeds and playback recordings from anywhere.
  • Multi-Site Management: Ideal for businesses or users with multiple properties, allowing easy management of several sites from one app.

ONVIF Support on UniFi Protect

As of recent updates, UniFi Protect now supports the ONVIF standard, allowing integration with third-party cameras. ONVIF (Open Network Video Interface Forum) is a global standard that ensures interoperability between IP-based security products. This addition broadens the range of compatible cameras, enabling users to connect non-UniFi devices to their UniFi Protect system.

However, while ONVIF cameras can stream video to UniFi Protect, they do not offer the full range of smart features, such as AI-driven motion detection or detailed alerts that UniFi cameras provide. Users will still benefit from basic video streaming and storage, but advanced event categorization (like vehicle or person detection) remains exclusive to UniFi’s native cameras.

This new feature is especially useful for those looking to incorporate legacy cameras into their system or they are slowly migrating to Unifi Camera’s whilst maintaining site security.


How UniFi Protect Compares to Third-Party Cameras

When evaluating third-party cameras like Hikvision and Reolink, UniFi Protect cameras offer several distinct advantages, especially within the UniFi ecosystem. Here are a few points of comparison:

  1. Hikvision vs UniFi G5 Pro

Resolution: Both offer 4K, but Hikvision tends to offer more specific outdoor-focused models.
Connectivity: Hikvision cameras often support both Ethernet and Wi-Fi, while the UniFi G5 Pro is Ethernet-only.
Key Difference: The seamless integration with the UniFi Protect system, alongside simplified central management, gives the G5 Pro an edge for users within the UniFi ecosystem.

  1. Reolink RLC-820A vs UniFi G5 Flex

Resolution: Both cameras offer high-definition video, with the Reolink at 4K and the G5 Flex at 2K HD.
Connectivity: Reolink supports Ethernet and Wi-Fi, making it more versatile for placement.
Key Difference: While Reolink is highly affordable, the G5 Flex wins in simplicity, particularly for users who already have a UniFi setup, which makes deployment and maintenance easier.


Conclusion

The updated UniFi Protect camera range offers a versatile set of cameras, each suited for different environments and use cases. Whether you’re looking for an entry-level camera for small indoor spaces, or a professional-grade outdoor camera with optical zoom, UniFi Protect has you covered.

While third-party options like Hikvision and Reolink may offer specific advantages, the integration and scalability of UniFi Protect make it the top choice for users already in the UniFi ecosystem.

Would you like more help selecting the perfect camera for your setup? Reach out to us today for expert advice!


A practical technology partner

Clear ownership across your whole IT environment

MSP247 brings day-to-day support, security, connectivity and planning together so your team has one accountable route for help.

Whole-environment support

Windows, Mac, iPhone, iPad, Chromebook, servers, networks and cloud services supported as one working environment.

Yorkshire coverage

Responsive remote support with planned on-site assistance across York, Leeds and the wider Yorkshire region.

A clearly agreed scope

Responsibilities, priorities, escalation routes and available response arrangements are explained before service begins.

Security and continuity

Accounts, devices, backups and connectivity resilience are reviewed together instead of as isolated products.

This site uses analytics.